> ## Documentation Index
> Fetch the complete documentation index at: https://docs.stackone.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Just-in-Time Provisioning
> Add users who aren't members of your organization yet when they sign in through SSO, and grant admin from an exact identity provider attribute match.
Just-in-time (JIT) provisioning adds a user who isn't already a member of your organization when they sign in through your SSO connection. There's no invitation to send and no directory push to configure. An assigned user who isn't a member yet signs in with SSO and joins your organization, existing StackOne users included.
JIT rides on your SSO connection, so [set up SSO](/identity/sso/overview) first. It's a lighter-weight alternative to [SCIM Provisioning](/identity/scim/overview). JIT adds a user at the moment of their sign-in. SCIM Provisioning creates members ahead of time from your directory.
## How JIT works
On every SSO sign-in, if the user isn't a member of your organization yet, StackOne:
* Adds them to your organization at the role your identity provider asserts, **Viewer** by default and **Admin** on an exact attribute match (see [Organization role](#organization-role-from-your-identity-provider)).
* Grants them the connection's **provisioned access**, the projects you selected at the roles you set.
Users who already have a StackOne account join the same way. Anyone who is already a member at sign-in is left untouched. Their role stays as it is, and access you removed from them isn't granted again. Adjust roles from the dashboard.
Removing a member doesn't keep them out while they can still sign in through your identity provider. They rejoin on their next sign-in as if provisioned for the first time. Unassign them from the StackOne application in your identity provider instead, or use **Disable Member** under **Organization > Manage Team**.
Only email addresses on the verified domain itself are provisioned. To link an existing StackOne account, its email address must be on the verified domain (or already be a trusted directory email from SCIM Provisioning).
A pending invitation always wins. If the user signing in has one for your organization, JIT steps aside and the invitation's role is used instead. SCIM Provisioning also takes precedence, so a user your directory already created keeps the membership it gave them.
## Organization role from your identity provider
By default, JIT provisions members as organization **Viewers**, the least-privilege role. To provision someone as an organization **Admin**, have your identity provider send a fixed attribute on the SSO assertion:
| Attribute | Value | Organization role |
| --------------- | -------------------------- | ----------------- |
| `stackone_role` | `admin` | Admin |
| `stackone_role` | any other value, or absent | Viewer |
The value is matched case-insensitively and trimmed, but it must be exactly `admin`. `admin`, `Admin`, and `ADMIN` all grant admin, while `administrator`, `admin-readonly`, an empty value, or a missing attribute all resolve to **Viewer**. StackOne never grants anything above organization admin from an identity provider attribute, so an unexpected value can only ever leave a member as a viewer.
Send `stackone_role` as a SAML attribute statement named exactly `stackone_role`. Send the value `admin` only for the people who should administer the organization, and leave the attribute off everyone else so they're provisioned as viewers.
This is the same mapping [SCIM Provisioning](/identity/scim/overview) uses: a SCIM `roles` value of `admin` provisions an organization admin, and everything else a viewer.
Organization admins can manage members, connections, and billing for the whole organization. Treat `stackone_role: admin` as you would any admin grant, and drive it from a group or rule in your identity provider that you already trust to define your StackOne admins.
## Prerequisites
* A verified SSO connection for your organization. JIT provisions members as they sign in through it. See [SSO overview](/identity/sso/overview).
* The **Org Admin** role to configure the defaults.
JIT is turned on per connection with the **Enable JIT** action, so nothing to request from support. The projects and roles you set are the connection's shared **provisioned access**: [SCIM Provisioning](/identity/scim/overview) applies the same set, so configuring it once covers both.
## Set up JIT
In the StackOne dashboard, go to **Organization > Security > SSO** and open your verified SSO connection. Select the **Provisioning** tab, then, on the **Provisioned access** card, select **Manage access**.
Pick the projects provisioned members should join and choose a role for each one (**Viewer**, **Member**, or **Admin**), then select **Save changes**. Pick the least-privilege role that fits each project. This sets project access only; the organization role comes from your identity provider.
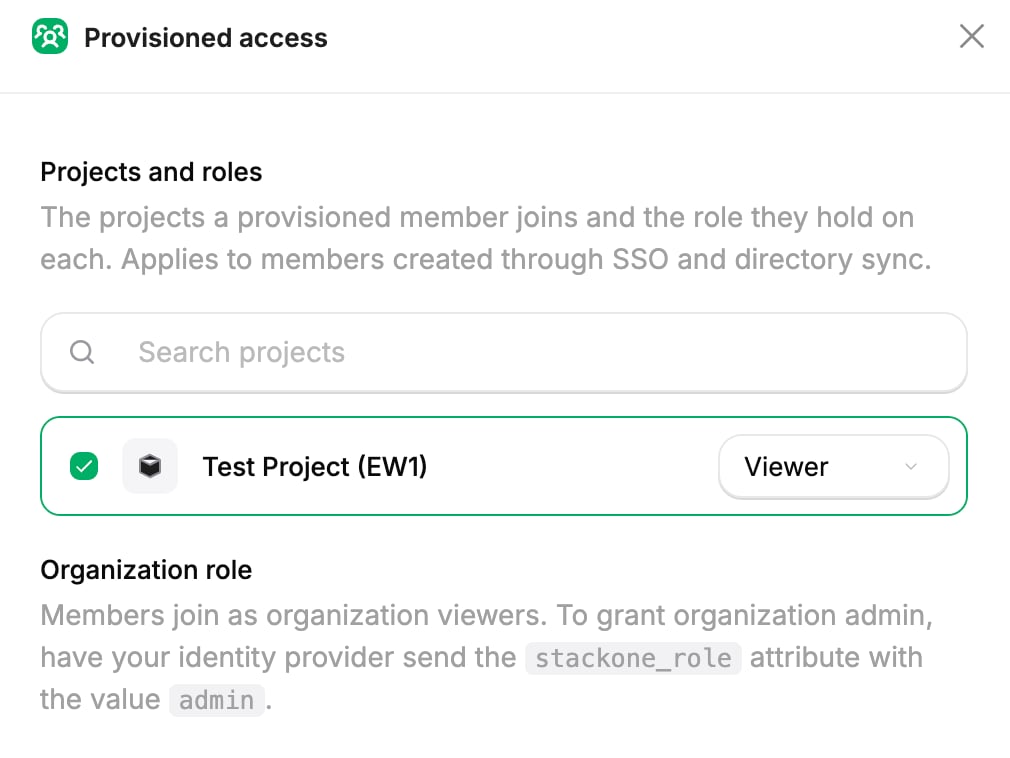 On the **Just-in-time provisioning** card, select **Enable JIT**. Provisioning starts on the next sign-in. If you haven't set any provisioned access yet, enabling JIT walks you through it first. A member is never provisioned into nothing.
To grant organization admin to specific people, configure your identity provider to send the `stackone_role` attribute with the value `admin` for them, as described in [Organization role](#organization-role-from-your-identity-provider). Leave it off everyone who should stay a viewer.
Assign the users to the StackOne application in your identity provider. On their next SSO sign-in, StackOne creates their membership at the organization role and provisioned access above.
## Next steps
Set up the SSO connection JIT provisions members through.
Provision members ahead of time from your directory over SCIM.
Grant many members the same project or account access at once.
Connect Okta as your SAML identity provider.